Page 1 of 8
GitHub Advanced Security for Azure DevOps — Overview
Vighnesh Notes · DevSecOps
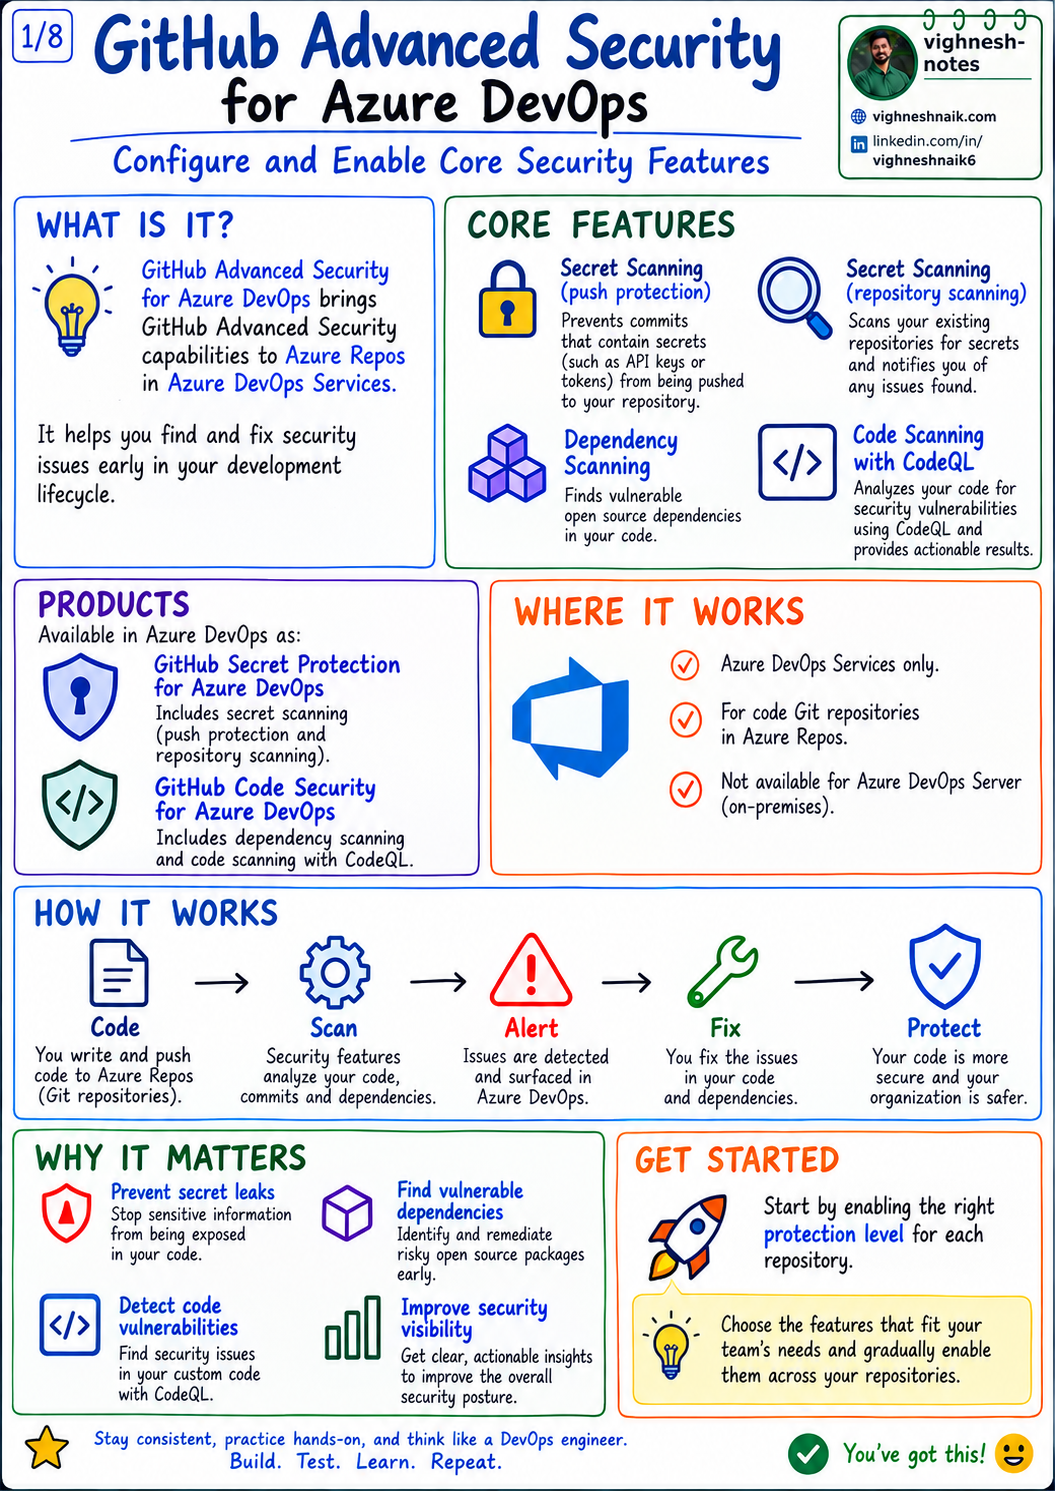
A visual implementation guide to Secret Protection, dependency scanning, CodeQL, pull request security checks, and secure repository onboarding in Azure DevOps.
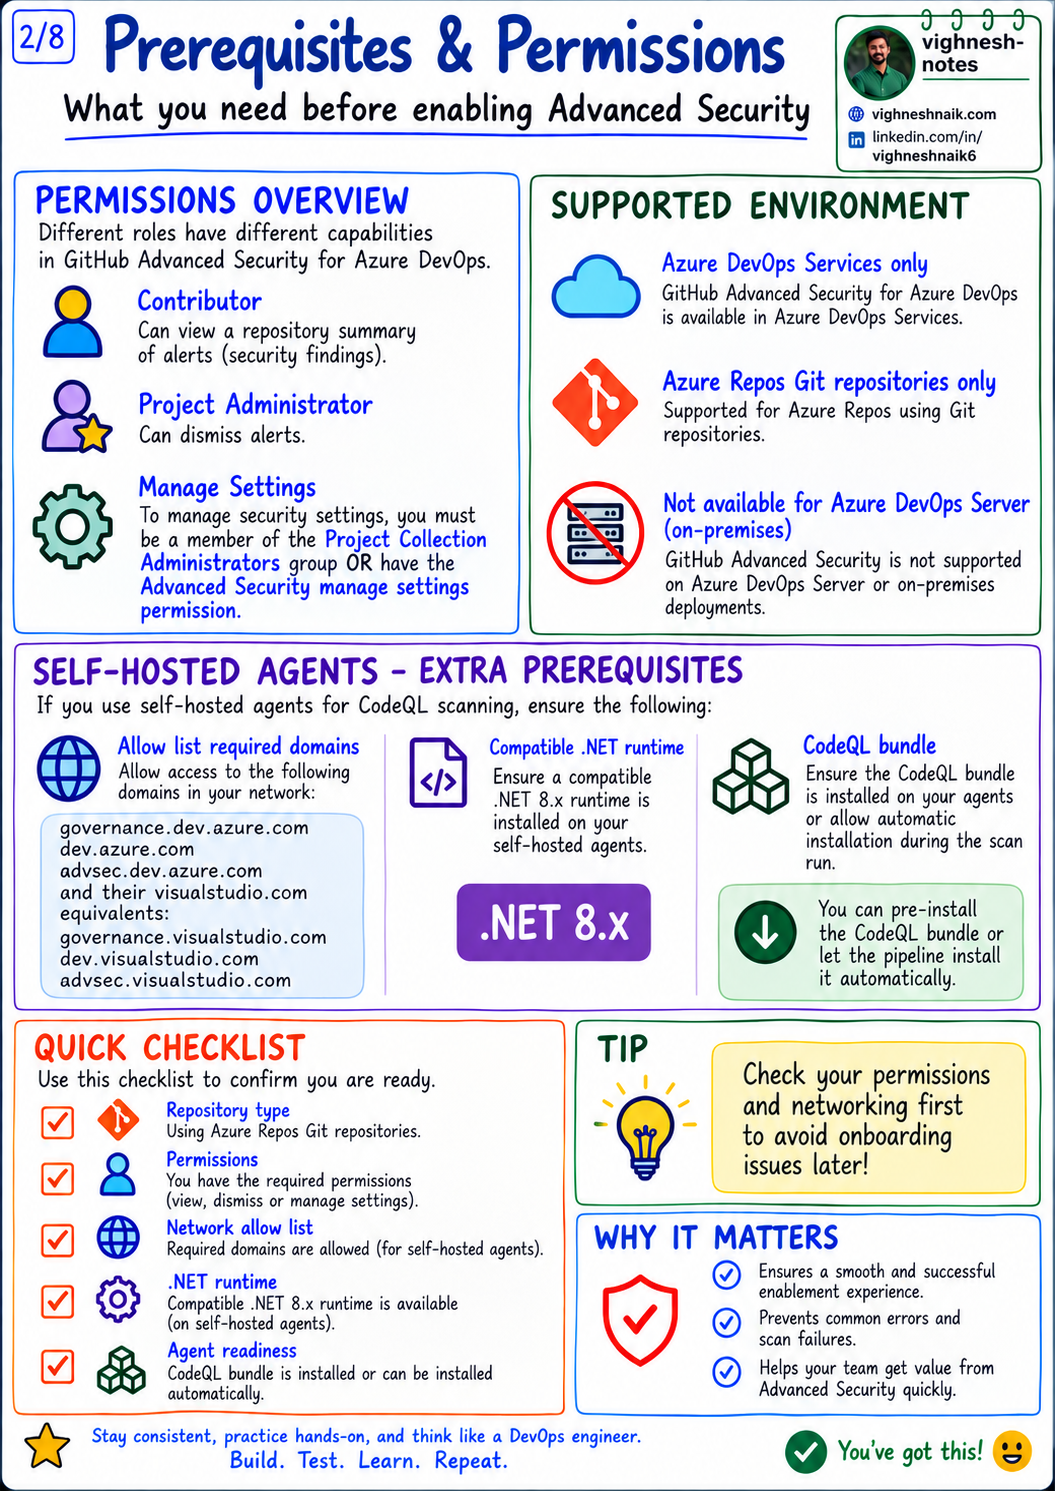
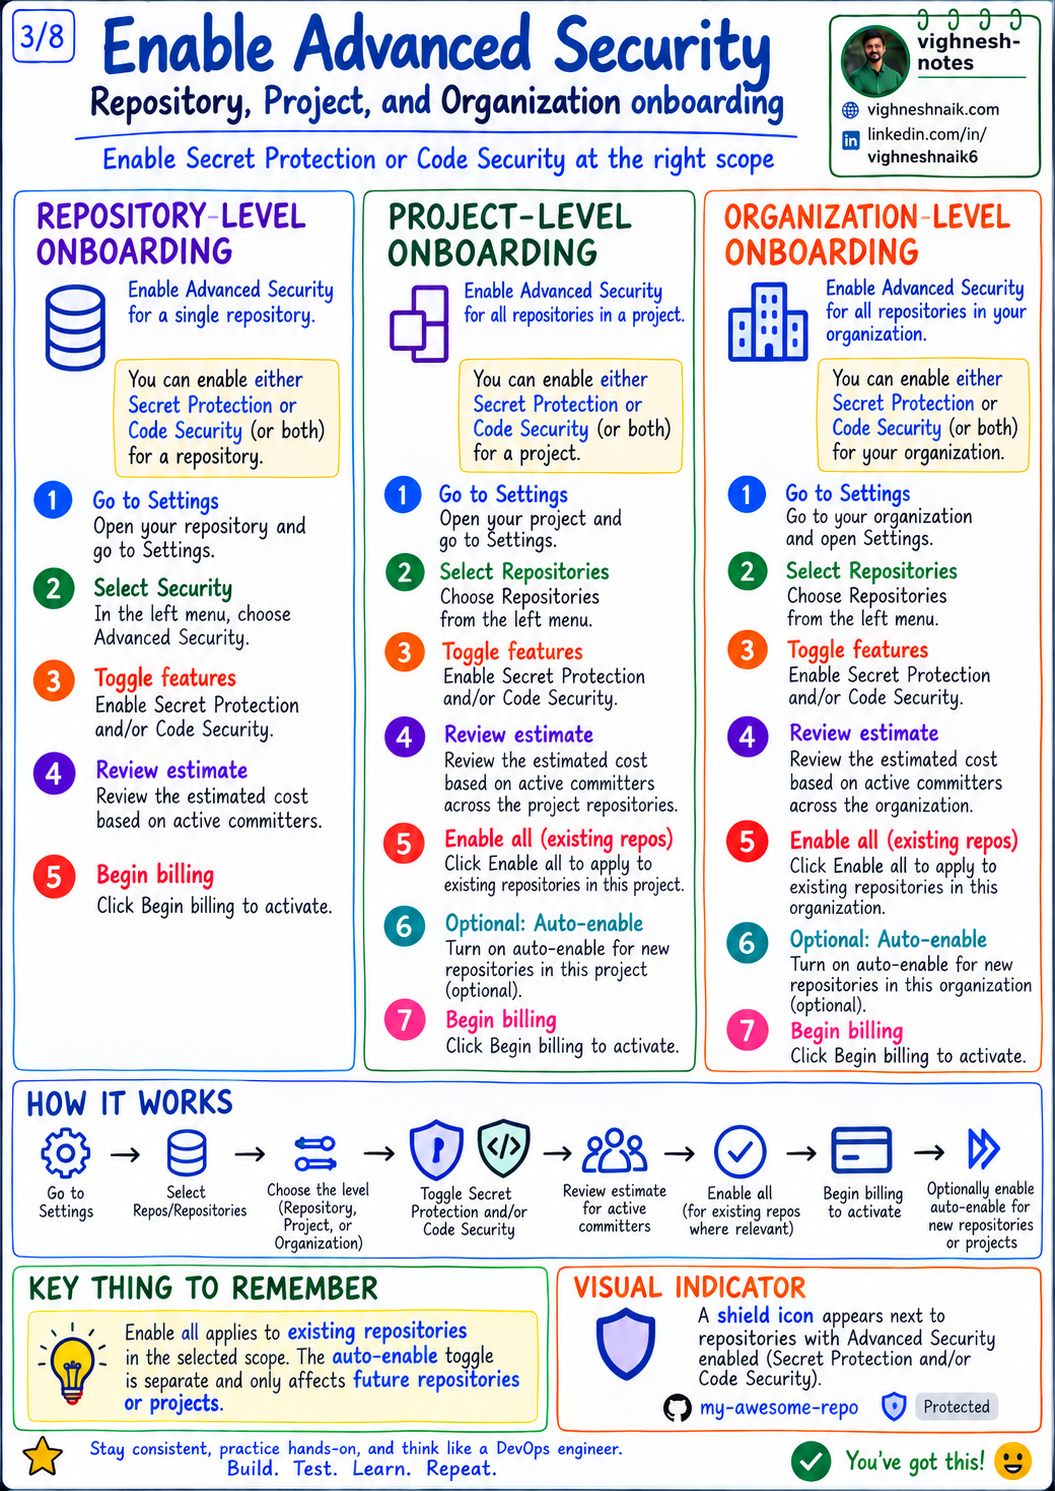
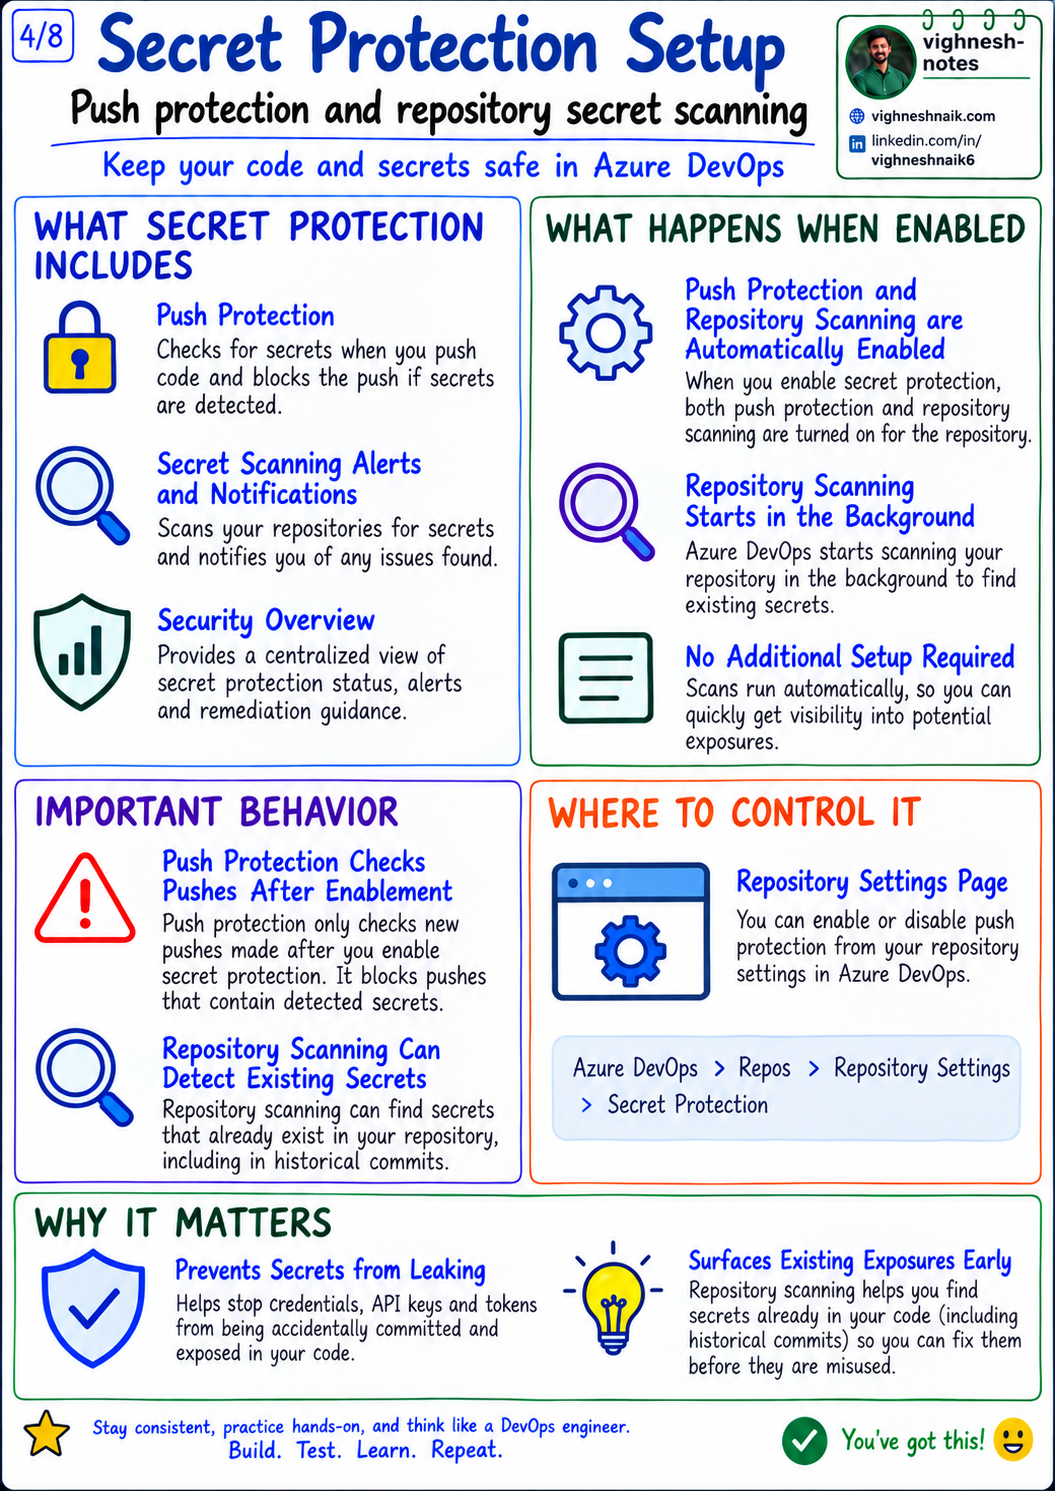
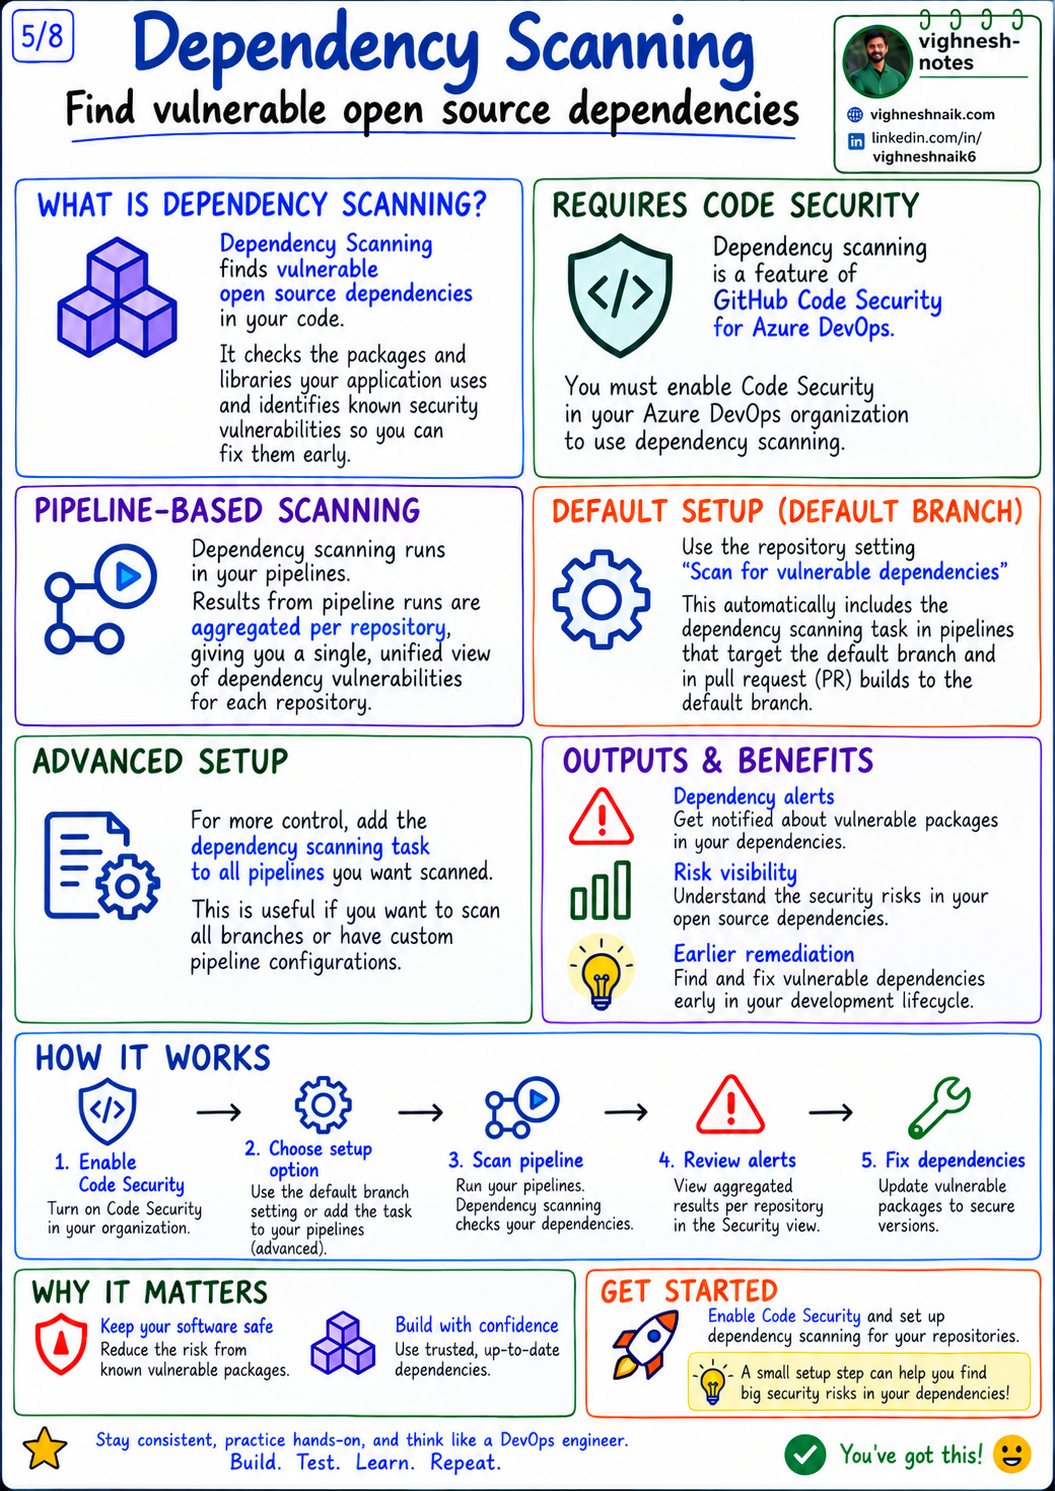
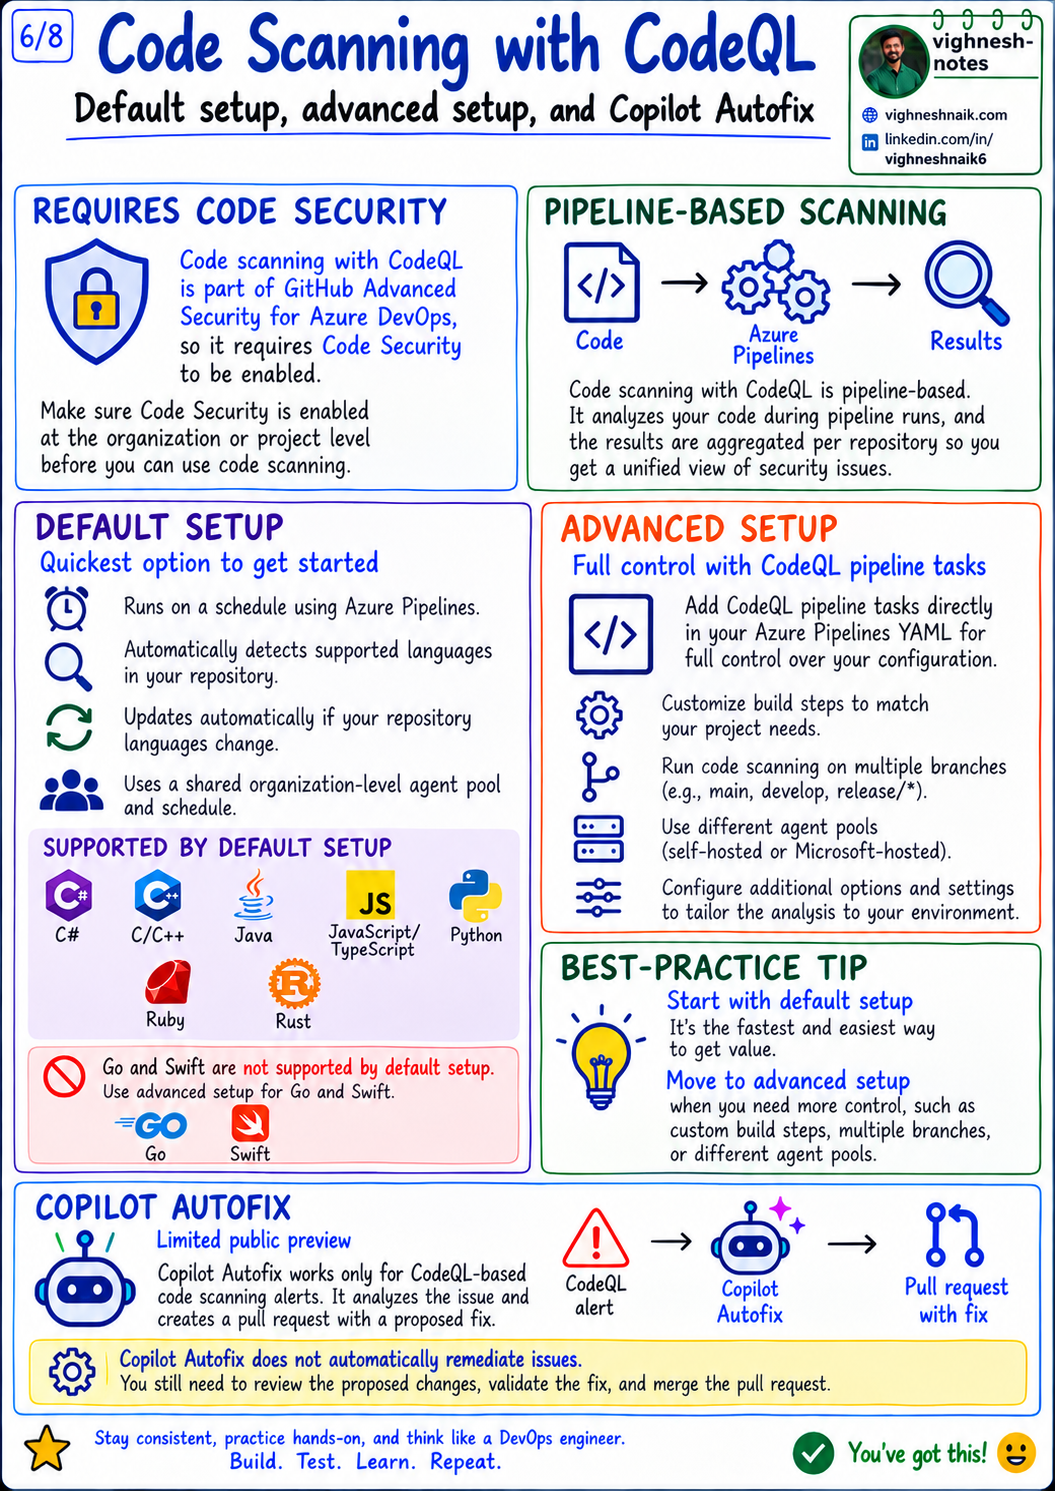
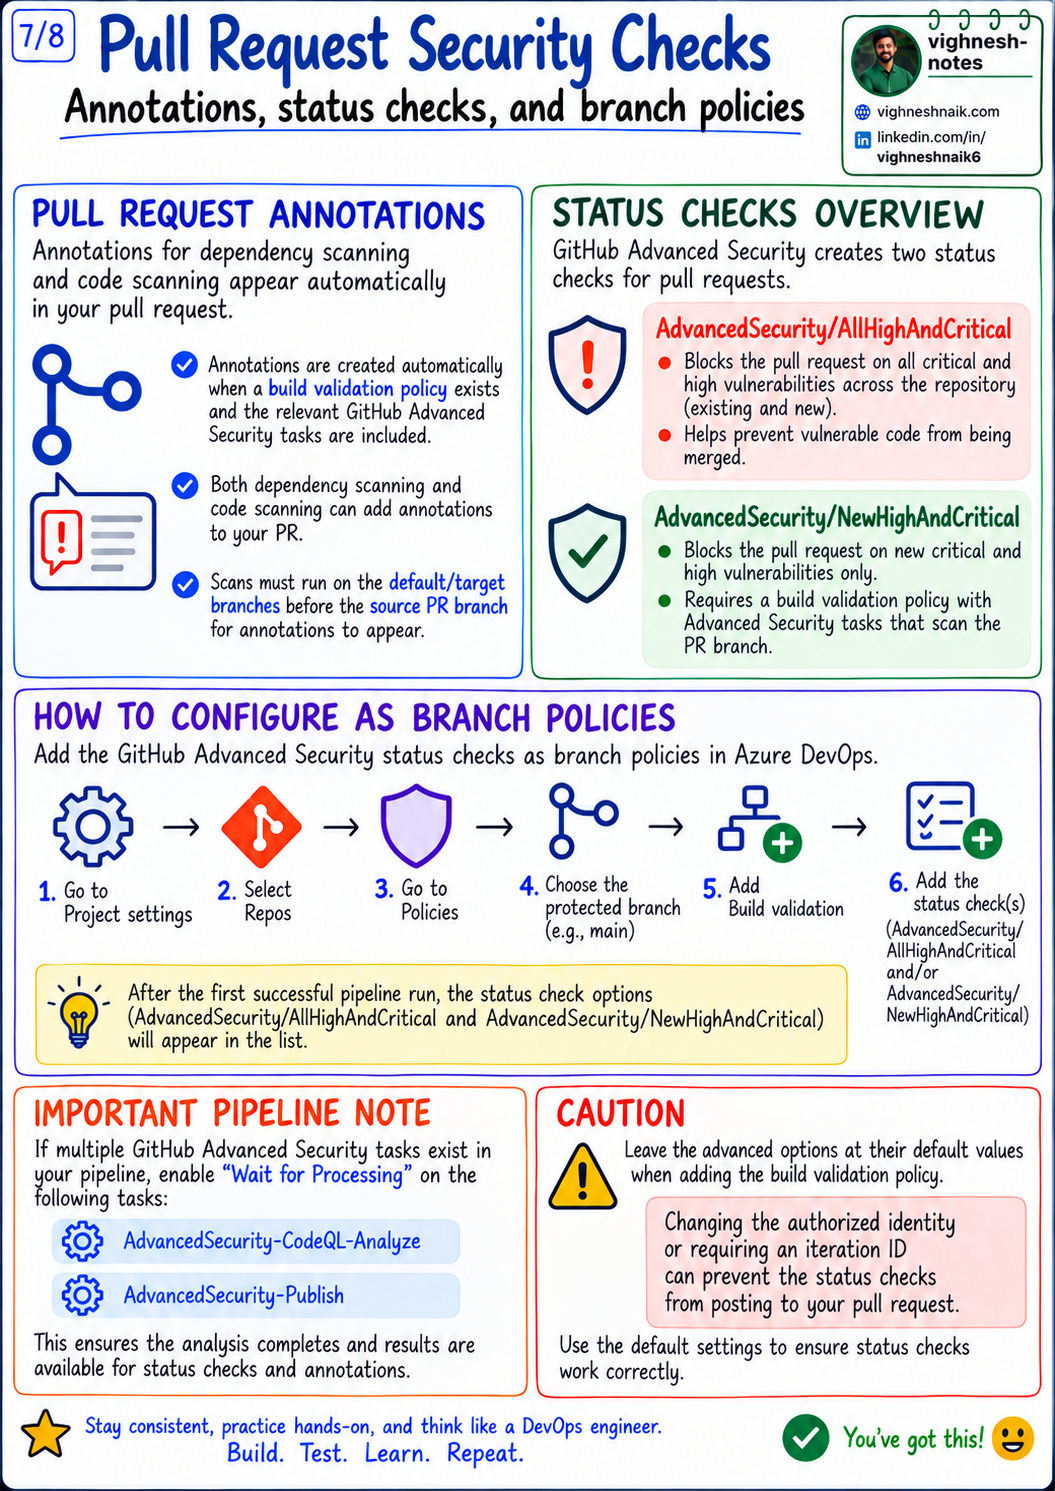
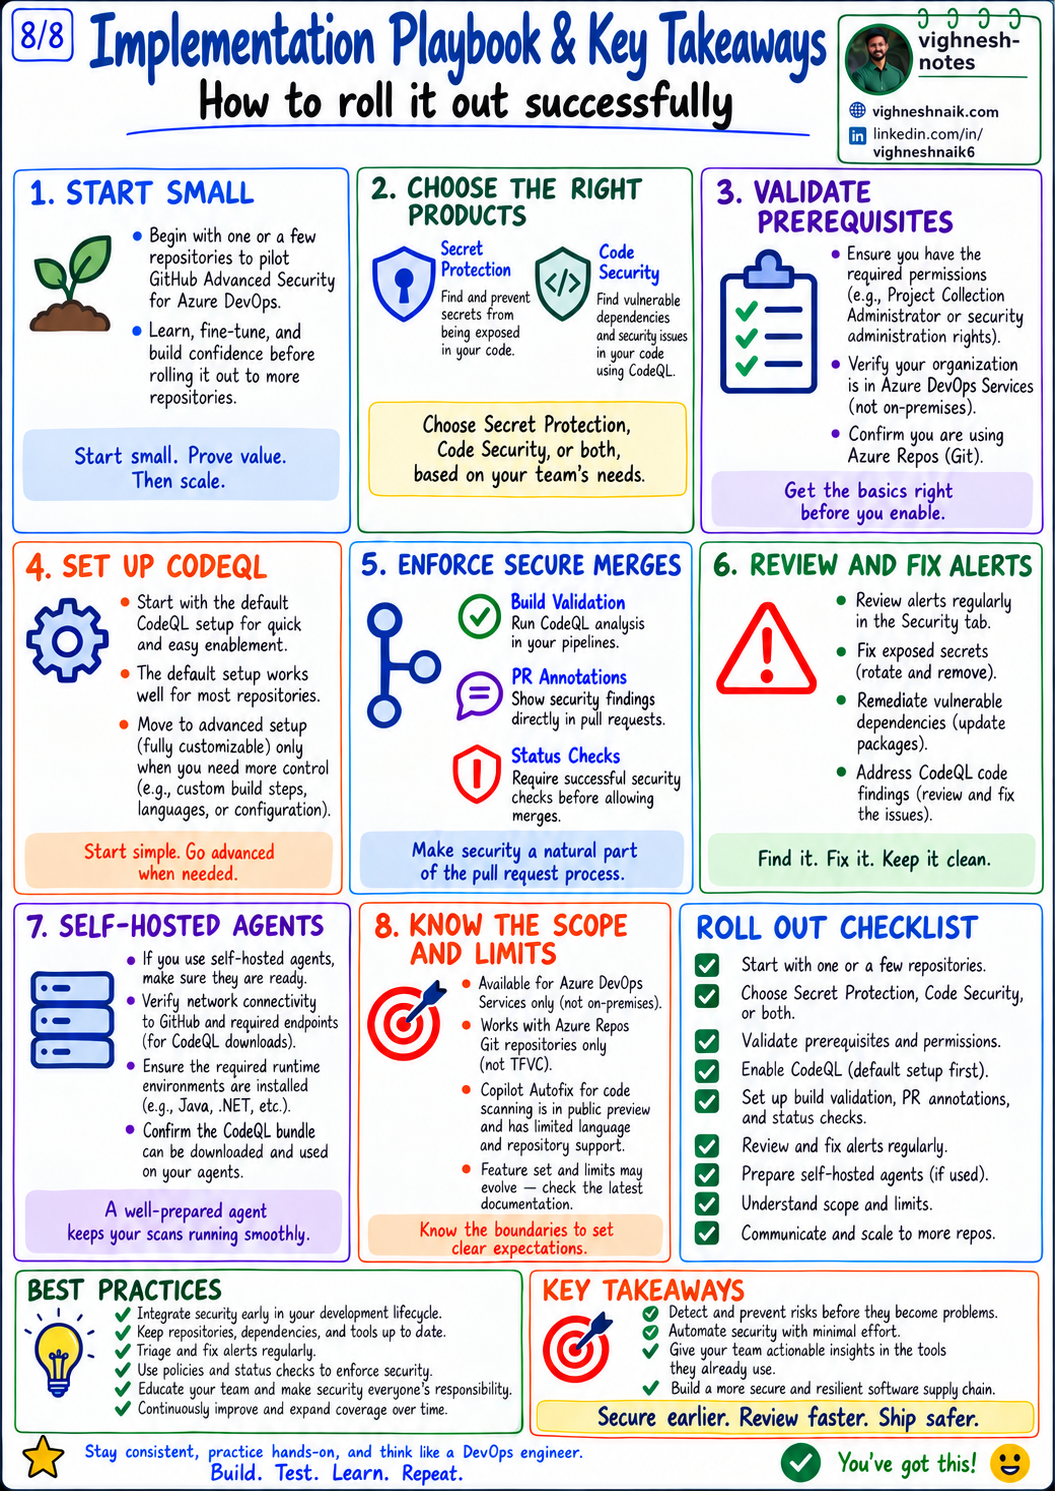
I created this eight-part visual guide to make GitHub Advanced Security for Azure DevOps easier to understand and implement. The series covers the available security products, prerequisites and permissions, repository/project/organization onboarding, secret protection, dependency scanning, CodeQL code scanning, pull request annotations, status checks, and practical rollout guidance.
These notes are designed as a study and implementation aid. Production environments should always be validated against current Microsoft Learn documentation, licensing, permissions, supported repository types, agent requirements, and organizational security policies.
GitHub Advanced Security for Azure DevOps brings several DevSecOps capabilities into Azure Repos, but the setup spans product enablement, repository onboarding, permissions, pipeline-based scanning, CodeQL, secret protection, pull request annotations, and branch policy enforcement. I created this visual series to make the implementation flow easier to understand and use as a practical reference.
This resource demonstrates Azure DevOps security knowledge, DevSecOps architecture, secret protection, software supply chain security, dependency scanning, CodeQL static analysis, pull request governance, branch policy design, security automation, and technical documentation.
These independent visual notes organize implementation concepts documented by Microsoft Learn. Microsoft and GitHub did not author, sponsor, review, or endorse this resource.
Microsoft Learn · Configure GitHub Advanced Security for Azure DevOpsThese are independent visual notes created by Vighnesh Naik and are not official Microsoft or GitHub documentation. Microsoft, Azure, Azure DevOps, GitHub, GitHub Advanced Security, CodeQL, and related product names are trademarks of their respective owners. Product capabilities, licensing, preview status, supported languages, permissions, and configuration steps can change. Always verify current information through official Microsoft Learn documentation before implementing security controls in production.